

[2026] Pass Microsoft MD-102 Exam Updated 394 Questions
Get 2026 Updated Free Microsoft MD-102 Exam Questions and Answer
Microsoft MD-102 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
NEW QUESTION # 94
Hotspot Question
You have devices enrolled in Microsoft Intune as shown in the following table.
You need to identify the following:
- Device you can remove from Intune by using the Wipe action.
- The enrollment state and the associated user account can be retained
on devices that are wiped.
What should you identify? To answer, select the appropriate options in the answer area.
Answer:
Explanation:
Explanation:
https://learn.microsoft.com/en-us/mem/intune/remote-actions/devices-wipe#supported-platforms- for-wipe-device-action
NEW QUESTION # 95
Hotspot Question
You have a Microsoft 365 subscription that uses Microsoft Intune Suite.
You use Microsoft Intune to manage devices.
You plan to create Windows 11 device builds for the marketing and research departments. The solution must meet the requirements:
- Marketing department devices must support Windows Update for
Business.
- Research department devices must have support for feature update
versions for up to 36 months from release.
What is the minimum Windows 11 edition required for each department? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Windows Update for Business is available in Windows 11 Pro, Enterprise, and Education.
Feature update versions are supported for 18 months in Windows 11 Pro and 36 months in Windows 11 Enterprise.
NEW QUESTION # 96
You have a Microsoft 365 subscription that contains a user named User1. The subscription contains devices enrolled in Microsoft intune as shown in the following table.
Microsoft Edge is available on all the devices.
Intune has the device compliance policies shown in the following table.
The Compliance policy settings are configured as shown in the exhibit. (Click the Exhibit tab.) You create the following Conditional Access policy:
* Name: Policy1
* Assignments
o Users and groups: User1
o Cloud apps or actions: Office 365 SharePoint Online
* Access controls
o Grant Require device to be marked as compliant
* Enable policy: On
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 97
You have SOO Windows 10 devices enrolled in Microsoft Intune.
You plan to use Exploit protection in Microsoft Intune to enable the following system settings on the devices:
* Data Execution Prevention (DEP)
* Force randomization for images (Mandatory ASlR)
You need to configure a Windows 10 device that will be used to create a template file.
Which protection areas on the device should you configure in the Windows Security app before you create the template file? To answer, drag the appropriate protection areas to the correct settings. Each protection area may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Exploit protection is a feature that helps protect against malware that uses exploits to infect devices and spread. Exploit protection consists of many mitigations that can be applied to either the operating system or individual apps1.
To configure a Windows 10 device that will be used to create a template file for Exploit protection, you need to configure the following protection areas on the device in the Windows Security app:
DEP: Device security. Data Execution Prevention (DEP) is a mitigation that prevents code from running in memory regions marked as non-executable. You can enable DEP system-wide or for specific apps in the Device security section of the Windows Security app1.
Mandatory ASLR: App & browser control. Force randomization for images (Mandatory ASLR) is a mitigation that randomizes the location of executable images in memory, making it harder for attackers to predict where to inject code. You can enable Mandatory ASLR system-wide or for specific apps in the App & browser control section of the Windows Security app1.
NEW QUESTION # 98
You have a Microsoft 365 E5 subscription that contains the groups shown in the following table.
You create a Conditional Access policy named CAPolicy1 that will block access to Microsoft Exchange Online from iOS devices. You assign CAPolicy1 to Group1.
You discover that User1 can still connect to Exchange Online from an iOS device.
You need to ensure that CAPolicy1 is enforced.
What should you do?
- A. Configure a new terms of use (TOU).
- B. Assign CAPolicy1 to Group2.
- C. Enable CAPolicy1
- D. Add a condition in CAPolicy1 to filter for devices.
Answer: B
Explanation:
Common signals that Conditional Access can take in to account when making a policy decision include the following signals:
* User or group membership
Policies can be targeted to specific users and groups giving administrators fine-grained control over access.
* Device
Users with devices of specific platforms or marked with a specific state can be used when enforcing Conditional Access policies.
Use filters for devices to target policies to specific devices like privileged access workstations.
* Etc.
Reference: https://learn.microsoft.com/en-us/azure/active-directory/conditional-access/overview
NEW QUESTION # 99
You have a server named Server1 and computers that run Windows 8.1. Server1 has the Microsoft Deployment Toolkit (MDT) installed.
You plan to upgrade the Windows 8.1 computers to Windows 10 by using the MDT deployment wizard.
You need to create a deployment share on Server1.
What should you do on Server1, and what are the minimum components you should add to the MDT deployment share? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Box 1: Install the Windows Deployment Services role.
Install and initialize Windows Deployment Services (WDS)
On the server:
Open an elevated Windows PowerShell prompt and enter the following command:
Install-WindowsFeature -Name WDS -IncludeManagementTools
WDSUTIL /Verbose /Progress /Initialize-Server /Server:MDT01 /RemInst:"D:\RemoteInstall" WDSUTIL /Set-Server /AnswerClients:All Box 2: Windows 10 image and task sequence only Create the reference image task sequence In order to build and capture your Windows 10 reference image for deployment using MDT, you will create a task sequence.
Reference: https://docs.microsoft.com/en-us/windows/deployment/deploy-windows-mdt/prepare-for-windows- deployment-with-mdt
https://docs.microsoft.com/en-us/windows/deployment/deploy-windows-mdt/create-a-windows-10-reference- image
NEW QUESTION # 100
You have a Microsoft 365 subscription.
You have 10 computers that run Windows 10 and are enrolled in mobile device management (MDM).
You need to deploy the Microsoft 36S Apps for enterprise suite to all the computers.
What should you do?
- A. From Azure AD. add an enterprise application.
- B. From the Microsoft Intune admin center, create a Windows 10 device profile.
- C. From Azure AD, add an app registration.
- D. From the Microsoft Intune admin center, add an app.
Answer: D
Explanation:
Explanation
To deploy Microsoft 365 Apps for enterprise to Windows 10 devices that are enrolled in Intune, you need to add an app of type "Windows 10 app (Win32)" in the Microsoft Intune admin center and configure the app settings. You can then assign the app to groups of users or devices. References:
https://docs.microsoft.com/en-us/mem/intune/apps/apps-win32-app-management
NEW QUESTION # 101
User1 and User2 plan to use Sync your settings.
On which devices can the users use Sync your settings? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Reference:
https://www.jeffgilb.com/managing-local-administrators-with-azure-ad-and-intune/
NEW QUESTION # 102
You have an on-premises Active Directory domain that syncs to Azure AD tenant.
The tenant contains computers that run Windows 10. The computers are hybrid Azure AD joined and enrolled in Microsoft Intune.
The Microsoft Office settings on the computers are configured by using a Group Policy Object (GPO).
You need to migrate the GPO to Intune.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
Explanation:
https://docs.microsoft.com/en-us/mem/intune/configuration/administrative-templates-windows
NEW QUESTION # 103
You have a Microsoft 365 subscription.
You use Microsoft Intune to manage devices.
You need to assess device performance during startup and identify any device models that take longer than average to start.
What should you use to assess the device performance, and which portal should you use? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 104
You need to recommend a solution to meet the device management requirements.
What should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://github.com/MicrosoftDocs/IntuneDocs/blob/master/intune/app-protection-policy.md
https://docs.microsoft.com/en-us/azure/information-protection/configure-usage-rights#do-not-forward-option-for-emails
Topic 2, Contoso, Ltd.
Overview
Contoso, Ltd. is a consulting company that has a main office in Montreal and branch offices in Seattle and New York.
Contoso has a Microsoft 365 E5 subscription.
Network Environment
The network contains an on-premises Active domain named Contoso.com. The domain contains the servers shown in the following table.
Contoso has a hybrid Azure Active Directory (Azure AD) tenant named Contoso.com.
Contoso has a Microsoft Store for Business instance.
Users and Groups
The Contoso.com tenant contains the users shown in the following table.
All users are assigned a Microsoft Office 365 license and an Enterprise Mobility + Security E3 license.
Enterprise State Roaming is enabled for Group1 and GroupA.
Group and Group have a Membership type of Assign
Devices
Contoso has the Windows 10 devices shown in the following table.
The Windows 10 devices are joined to Azure AD and enrolled in Microsoft intune.
The Windows 10 devices are configured as shown in the following table.
All the Azure AD joined devices have an executable file named C:\AppA.exe and a folder named D:\Folder 1.
Microsoft Endpoint Manager Configuration
Microsoft Endpoint Manager has the compliance policies shown in the following table.
The Compliance policy settings are shown in the following exhibit.
The Automatic Enrolment settings have the following configurations:
* MDM user scope GroupA
* MAM user scope: GroupB
You have an Endpoint protection configuration profile that has the following Controlled folder access settings:
* Name: Protection1
* Folder protection: Enable
* List of apps that have access to protected folders: CV\AppA.exe
* List of additional folders that need to be protected: D:\Folderi1
* Assignments
Windows Autopilot Configuration
Currently, there are no devices deployed by using Window Autopilot
The Intune connector tor Active Directory is installed on Server 1.
Planned Changes
Contoso plans to implement the following changes:
* Purchase a new Windows 10 device named Device6 and enroll the device in Intune.
* New computers will be deployed by using Windows Autopilot and will be hybrid Azure AO joined.
* Deploy a network boundary configuration profile that will have the following settings:
* Name Boundary 1
* Network boundary 192.168.1.0/24
* Scope tags: Tag 1
* Assignments;
* included groups: Group 1. Group2
* Deploy two VPN configuration profiles named Connection! and Connection that will have the following settings:
* Name: Connection 1
* Connection name: VPNI
* Connection type: L2TP
* Assignments:
* Included groups: Group1. Group2, GroupA
* Excluded groups: -
* Name: Connection
* Connection name: VPN2
* Connection type: IKEv2 i Assignments:
* included groups: GroupA
* Excluded groups: GroupB
* Purchase an app named App1 that is available in Microsoft Store for Business and to assign the app to all the users.
Technical Requirements
Contoso must meet the following technical requirements:
* Users in GroupA must be able to deploy new computers.
* Administrative effort must be minimized.
NEW QUESTION # 105
You have a Microsoft 365 E5 subscription.
You use Microsoft Intune to manage all Windows 11 devices.
You create an attack surface reduction (ASR) policy named Profile1 based on the Attack Surface Reduction Rules profile and assign Profile! to all the devices.
A user reports that an Adobe Reader plug-in is now blocked.
You need to ensure that the plug-in is unblocked.
What should you do?
- A. Configure ASR Only Per Rule Exclusions in Profile1.
- B. Create a device compliance policy and assign the policy to all the devices.
- C. Create an Endpoint Privilege Management policy and assign the policy to all the devices.
- D. Add a scope tag to Profile1.
Answer: A
NEW QUESTION # 106
You need to meet the technical requirements for the LEG department computers.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
Explanation:
Reference:
https://docs.microsoft.com/en-us/windows/deployment/update/windows-analytics-azure-portal
NEW QUESTION # 107
What should you use to meet the technical requirements for Azure DevOps?
- A. Windows Information Protection (WIP)
- B. An app protection policy
- C. A device configuration profile
- D. Conditional access
Answer: C
Explanation:
References:
https://docs.microsoft.com/en-us/azure/devops/organizations/accounts/manage-conditional-access?
view=azure-devops
NEW QUESTION # 108
You have a Microsoft 365 subscription.
You have devices enrolled in Microsoft Intune as shown in the following table.
To which devices can you deploy apps by using Intune?
- A. Device1, Device2, Device3, and Device4
- B. Device1 and Device3 only
- C. Device1 only
- D. Device1 and Device2 only
- E. Device1, Device2, and Device3 only
Answer: E
Explanation:
When it comes to apps, Intune supports the following platforms:
Windows
iOS/iPadOS
macOS
Android
https://learn.microsoft.com/en-us/microsoft-365/solutions/apps-add-step-1?view=o365- worldwide#determine-the-platforms-needed-for-each-app
NEW QUESTION # 109
You have 200 computers that run Windows 10. The computers are joined to Microsoft Azure Active Directory (Azure AD) and enrolled in Microsoft Intune.
You redirect Windows known folders to Microsoft OneDrive for Business.
Which folder will be included in the redirection?
- A. Music
- B. Downloads
- C. Saved Games
- D. Documents
Answer: D
Explanation:
There are two primary advantages of moving or redirecting Windows known folders (Desktop, Documents, Pictures, Screenshots, and Camera Roll) to Microsoft OneDrive for the users in your domain:
Your users can continue using the folders they're familiar with. They don't have to change their daily work habits to save files to OneDrive.
Saving files to OneDrive backs up your users' data in the cloud and gives them access to their files from any device.
Reference:
https://docs.microsoft.com/en-us/onedrive/redirect-known-folders
NEW QUESTION # 110
You have a Microsoft 365 E5 subscription that contains the users shown in the following table.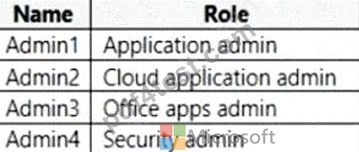
In the Microsoft 365 Apps admin center, you create a Microsoft Office customization.
Which users can download the Office customization file from the admin center?
- A. Admin1 and Admin3 only
- B. Admin1, Admin2, Admin3. and Admin4
- C. Admin3 and Admin4 only
- D. Admin3 only
- E. Admin1, Admin2, and Admin3 only
Answer: C
Explanation:
* Admin1
An application admin has full access to enterprise applications, applications registrations, and application proxy settings.
* Admin2
Mark your app as publisher verified.
In Azure AD this user must be a member of one of the following roles: Application Admin, Cloud Application Admin, or Global Admin.
* Admin3
Office Apps admin - Assign the Office Apps admin role to users who need to do the following:
- Use the Office cloud policy service to create and manage cloud-based policies for Office
- Create and manage service requests
- Manage the What's New content that users see in their Office apps
- Monitor service health
Reference:
Office Apps admin - Assign the Office Apps admin role to users who need to do the following
https://docs.microsoft.com/en-us/azure/active-directory/develop/mark-app-as-publisher-verified
NEW QUESTION # 111
You have a Microsoft 365 E5 subscription that contains 10 Android Enterprise devices. Each device has a corporate-owned work profile and is enrolled in Microsoft Intune.
You need to configure the devices to run a single app in kiosk mode.
Which Configuration settings should you modify in the device restrictions profile?
- A. System security
- B. Users and Accounts
- C. General
- D. Device experience
Answer: D
Explanation:
To configure the devices to run a single app in kiosk mode, you need to modify the Device experience settings in the device restrictions profile. You can specify the app package name and activity name for the app that you want to run in kiosk mode. References: https://docs.microsoft.com/en-us/mem/intune/configuration
/device-restrictions-android-for-work#device-experience
NEW QUESTION # 112
You have a Microsoft 365 E5 subscription that contains 150 hybrid Azure AD joined Windows devices. All the devices are enrolled in Microsoft Intune. You need to configure Delivery Optimization on the devices to meet the following requirements:
* Allow downloads from the internet and from other computers on the local network.
* Limit the percentage of used bandwidth to 50.
What should you use?
- A. an Update ring for Windows 10 and later profile
- B. a Windows Update for Business Group Policy setting
- C. a configuration profile
- D. a Microsoft Peer-to-Peer Networking Services Group Policy setting
Answer: C
Explanation:
A configuration profile is the correct answer because it allows you to configure Delivery Optimization settings for Windows devices in Intune. You can specify the download mode, bandwidth limit, caching options, and more. A configuration profile is a template that contains one or more settings that you can apply to groups of devices. Reference:
Windows 10 Delivery Optimization settings for Intune - Microsoft Intune | Microsoft Learn Delivery Optimization settings in Microsoft Intune
NEW QUESTION # 113
Hotspot Question
You have unrooted devices enrolled in Microsoft Intune as shown in the following table.
The devices are members of a group named Group1.
In Intune, you create a device compliance location that has the following configurations:
Name: Network1
IPv4 range: 192.168.0.0/16
In Intune, you create a device compliance policy for the Android platform. The policy has following configurations:
Name: Policy1
Device health: Rooted devices: Block
Locations: Location: Network1
Mark device noncompliant: Immediately
Assigned: Group1
In Intune device compliance policy has the following configurations:
Mark devices with no compliance policy assigned as: Compliant
Enhanced jailbreak detection: Enabled
Compliance status validity period (days): 20
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
D1: compliant because of "mark devices with no compliance policy assigned as compliant" D2: Not compliant because of the IP subnet D3 compliant OS is android and IP subnet is in Network 1 location
NEW QUESTION # 114
You have a Microsoft 365 E5 subscription.
You create an app protection policy for Android devices named Policy1 as shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Box 1: Install the Intune Company Portal app on the device
On Android, Android devices will prompt to install the Intune Company Portal app regardless of which Device type is chosen.
Bix 2: Devices only
For Android devices, unmanaged devices are devices where Intune MDM management has not been detected.
This includes devices managed by third-party MDM vendors.
Reference: https://docs.microsoft.com/en-us/mem/intune/apps/app-protection-policies#app-protection- policies-for-iosipados-and-android-apps
NEW QUESTION # 115
Hotspot Question
You have a Microsoft 365 E5 subscription.
You need to route Microsoft Intune logs to an Azure resource that supports the use of visuals, monitoring, and alerting.
Which settings should you configure in Intune, and which resource should you use? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 116
Hotspot Question
You have a Microsoft 365 E5 subscription.
You create a new update rings policy named Policy1 as shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
"The new policy starts the countdown for the update installation deadline from when the update is published plus any deferral."
https://learn.microsoft.com/en-us/windows/deployment/update/update-policies The update is available to market, there is then a deferral of 30 days, which then makes it available for a device, once the device has found the update there will be a deadline for 30 days to install and reboot. 60 days total.
Otherwise, the 30 day deadline and 30 day deferral would line up and all devices would be required to install and reboot same day.
NEW QUESTION # 117
......
Verified MD-102 exam dumps Q&As with Correct 394 Questions and Answers: https://www.pdf4test.com/MD-102-dump-torrent.html
MD-102 Dumps PDF and Test Engine Exam Questions: https://drive.google.com/open?id=1VRzH6dMDwLwhuZFoDR0eWnBYLi4J56we
